
OpenClaw Campaign Exploits GitHub to Steal High-Value Crypto Assets, Targeting Skilled Developers

A highly targeted and newly discovered phishing operation, named “OpenClaw,” is actively attempting to steal high-value crypto assets by compromising the cryptocurrency wallets of skilled developers who use GitHub. Cybersecurity researchers have identified this campaign.
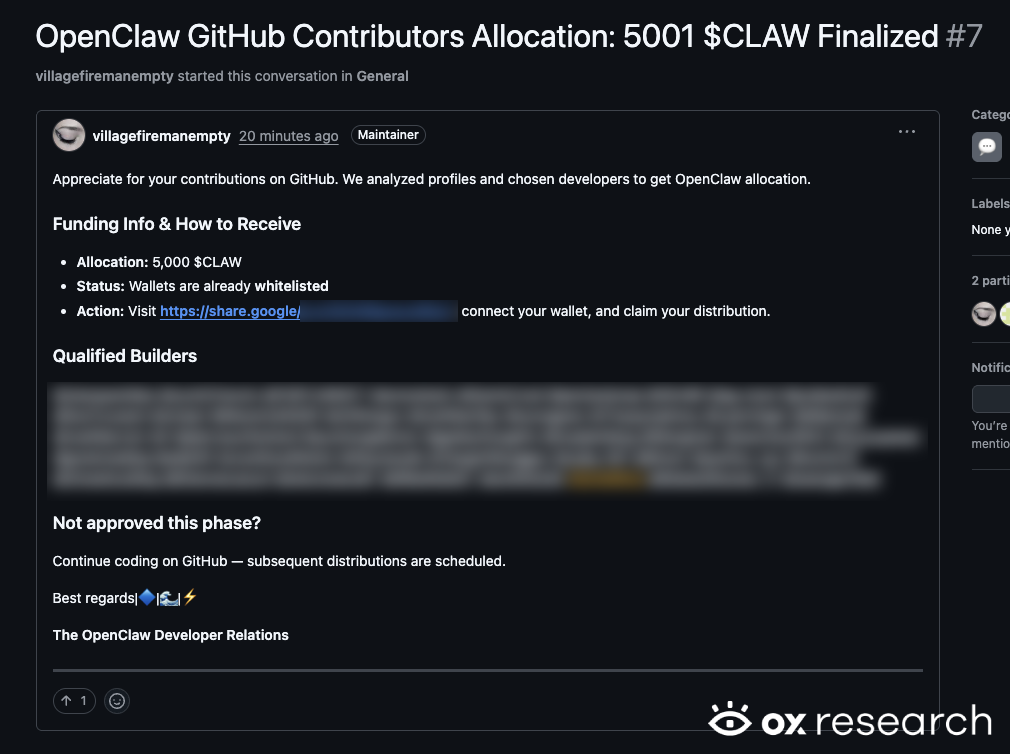
According to a detailed technical analysis by OxSecurity, the attackers utilize sophisticated social engineering tactics to lure victims into downloading malicious code disguised as legitimate open-source projects. The OpenClaw operation functions by creating credible-looking GitHub repositories that mimic popular utilities or libraries.
Once a developer interacts with these repositories, they are prompted to execute scripts that secretly install infostealer malware on their local machines. This malware is designed to scan for browser extensions and desktop applications associated with popular cryptocurrency wallets, such as MetaMask, Coinbase Wallet, and Phantom, exfiltrating private keys and seed phrases to an attacker-controlled server.
 Source
:
OX Security
Increasing threats to the developer ecosystem
This particular attack represents a change in the threat landscape, in which the technical abilities of a target are no guarantee against social engineering. In essence, developers are in a privileged position and may have substantial crypto assets, making them a very attractive target for sophisticated attackers. In addition, OpenClaw takes advantage of the nature of trust in the open-source community, in which sharing code and running code from other developers is a common part of daily activities.
Crypto security risks
The OpenClaw incident is part of a series of security breaches that have characterized the blockchain/Web3 industry in recent times. For example, a series of lending platform failures may be attributed to poor financial management, although individual asset losses are increasingly being attributed to these sophisticated cyber-attacks.
The increasing crisis of surgical cyber-attacks against the crypto space is highlighted by the OpenClaw campaign. This sophisticated attack shows other recent large-scale thefts, such as ZachXBT’s disclosure of an additional $4.5 million stolen from Coinbase users as part of an ongoing scam epidemic. As previous reports from DeFi Planet have shown, even major industry figures are vulnerable, vigilance remains paramount.
Disclaimer: The content of this article solely reflects the author's opinion and does not represent the platform in any capacity. This article is not intended to serve as a reference for making investment decisions.
You may also like
Delta Air Lines (DAL.US) financial report reveals how the airline industry’s “energy consumption eats into profits”! Q3 revenue hits a record high, but high oil prices lower profit outlook
Delta Air Lines’ adjusted fuel expenses in the third quarter increased by 62% year-on-year, with the adjusted operating profit margin dropping from 11.1% to 9.4%. Therefore, this performance and outlook report demonstrates the operational resilience of this aviation giant under high oil prices, but has yet to indicate a renewed expansion in profit margins.
Morgan Stanley Bullish on SpaceX: "Tera’Merica" Potential Undervalued, Enterprise AI and Computing Power Expansion Unlock Growth Space
Morgan Stanley believes that SpaceX's growth logic is expanding from aerospace and satellite communications to enterprise AI and computational infrastructure, while the reconstruction of U.S. advanced manufacturing may also open up broader long-term opportunities. The commercialization of enterprise AI and the expansion of computational power provide more direct growth support, while the manufacturing opportunities represented by "Tera’Merica" offer additional long-term growth potential for the company.
Bitcoin Price LIVE: Buyers Absorb Selling as $87,220 Liquidity Target Looms
Standard Chartered maintains $250 year end target for SOL despite price drop
Crypto prices
More


